


What Is a Digital Signature?
A digital signature is a more secure type of electronic signature that are cryptographically bound to the document, creating a unique digital “footprint” that verifies the signer’s identity and ensures that the content remains unaltered. This is enabled by digital certificates obtained from a trusted third-party and ensures that it is unaltered.
Digital Signatures vs. Electronic Signatures
What separates digital signatures from other e-signatures, and even other signing methods like wet signatures, is its underlying technology that ensures authenticity and integrity. Digital signatures use technical components such as public key infrastructure (PKI) and digital certificates to establish a verifiable link between the signer and the document.
In simple terms, digital signatures authenticate the signer’s identity and detect whether the document has been altered after signing. Other forms of electronic signatures, such as a scanned image of a wet-ink signature placed on a PDF or Word document, generally do not provide these same cryptographic protections and often pose security and legal risk to businesses.
What Is a Public Key Infrastructure?
PKI is a system that manages encryption keys to enable secure communication and identity verification. It provides the security infrastructure behind digital signatures and operates through a pair of linked keys:
- Private Key: Known only to the signer. This key encrypts the document’s hash (a condensed version of the document’s data — think of it like a unique “digital fingerprint”). This creates the digital signature, binding the signer’s identity to the document.
- Public Key: Shared with the recipients. This key is used to decrypt the signature and verifies that the document’s hash matches its original state.
This dual-key process ensures that the signer is authenticated and that any unauthorized changes to the document after it has been signed will invalidate the signature.
What Are Digital Certificates?
A digital certificate is an electronic file issued by a Certificate Authority (a trusted and accredited third party) that acts as evidence of a signer’s identity. While a PKI provides the mechanism for signing, digital certificates provide the validation of identity.
To accommodate different levels of risk, digital signatures are generally categorized into three different classes:
- Class 1 – These certificates offer a basic level of security. They are best suited for environments or circumstances where there is a very low risk of data compromise or identity theft.
- Class 2 – These certificates authenticate a signer’s identity against a pre-verified database. They are appropriate for transactions involving a moderate risk of data compromise and are often used for tax documents or corporate filings.
- Class 3 - These digital certificates are considered the most secure of the three classes. They are reserved for high-stakes matters such as trading, e-commerce, or any transaction involving large sums of money and highly confidential information.
How Do Digital Signatures Work?
PKI and digital certificates work together to keep digital signatures secure through a four-step process:
Step #1: Document Hashing
A hash is created from the document’s content. This hash acts as a digital "fingerprint" of the document, capturing its exact state at the time of signing. Even the slightest alteration to the document, such as a single character change, would generate an entirely different hash that makes it easy to detect tampering.
Step #2: Encryption
The signer’s private key is used to encrypt the hash, creating the digital signature. This signature is unique to both the document and the signer, ensuring that the identity of the signer is tied directly to the document. The encrypted hash adds a layer of security, as only the signer’s private key can create it, and only the corresponding public key can decrypt it.
Step #3: Document Transmission
The signed document, along with its encrypted hash (the digital signature) and the signer’s digital certificate, is transmitted to the recipient. This digital certificate contains the signer’s public key and identity information, and issued by a trusted Certificate Authority. At this point, the document is considered tamper-evident, as any unauthorized modifications would invalidate the signature.
Step #4: Verification
Upon receiving the document, the recipient’s system (the digital signing platform used) first verifies the digital certificate by checking its validity and confirming that it was issued by a trusted Certificate Authority.
Once the certificate is validated, the recipient’s system uses the signer’s public key from the certificate to verify the digital signature and recover the original hash (the hash created at the time of signing).
The recipient’s system then generates a new hash from the received document using the same hash function. This is done by reprocessing the entire received document exactly as it exists at that moment.
If the two hashes match, it confirms that:
- The document has not been altered.
- The signature is valid and tied to the signer’s private key.
This verification process ensures both the authenticity of the signer and the integrity of the document, providing a high level of trust and security.
How To Create a Digital Signatures
For most individuals and businesses, digital signatures are typically created through digital signature solutions. These platforms already have the technology needed to create and protect digital signatures, such as encryption, digital certificates, audit trails, and other security features. As such, users do not need to set up the technical architecture themselves.
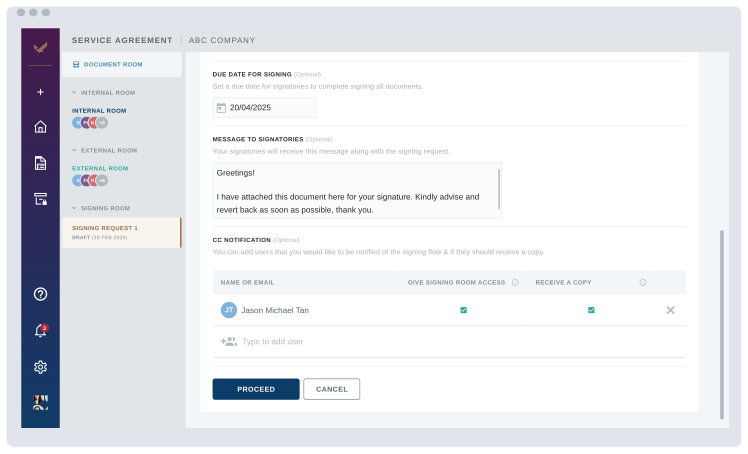
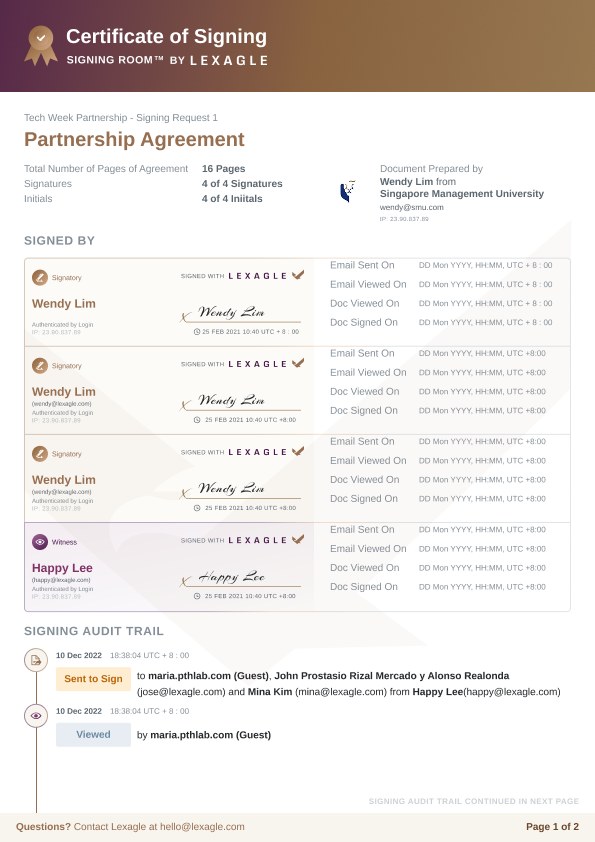
For instance, in Lexagle, users just need to type, draw, or upload their signatures within the platform. The system handles the security measures in the background, including encryption and recording who accessed and signed the document, how they were authenticated, and exactly when each action took place.
In 2026, there are numerous digital signature solutions to choose from. To help you compare your options, we reviewed 12 of the best digital signature solutions in 2026.
Can You Remove a Digital Signature After Signing?
Yes, but with nuance, such as whose signature you want to remove or whether the document has been finalized.
If you are still in your turn of signing, you may be able to remove or replace your own digital signature in the signature field, depending on the digital signature platform. However, once other parties have signed, you generally cannot remove or alter their signatures. You also cannot simply remove your signature from a finalized agreement and change the document without affecting its signature validity. This is an important safeguard provided by digital signatures against unauthorized changes and document tampering.
If you need to change the terms of a finalized agreement, you can use a contract amendment to modify or remove existing provisions. If you simply need to add new or supplementary terms, you can use a contract addendum. These documents formally record the agreed changes and help establish which terms govern the parties going forward.
What Are the Benefits of Digital Signatures?
1. Ensures Document Authenticity and Integrity
The primary purpose of digital signatures is to verify that each signature is authentic and that documents and contracts have not been altered after signing. Their tamper-evident seals help protect against forgery and unauthorized changes. With AI-generated content making identity verification and document authentication increasingly important, these security measures can help protect your business from disputes over who signed a document or whether its contents were altered.
2. Environmentally-Friendly
Signing with digital signatures reduces the need for physical paperwork, which reduces paper consumption and waste. This not only supports your company’s sustainability initiatives but also minimizes the environmental impact of wet signature processes.
3. Legally Recognized Worldwide
Digital signatures are widely accepted under international regulations, including the US ESIGN Act and eIDAS framework. In fact, as global commerce continues to digitize, an increasing number of jurisdictions are expanding their acceptance of digital signatures, especially with the rise of remote online notarization. While enforceability can vary based on jurisdiction or contract type, digital signatures remain a go-to for a majority of businesses with cross-border agreements
4. Accelerated Contract Cycles and Cost Efficiency
Digital signatures can significantly reduce the time and effort involved in the traditional contract signing process, eliminating many of the delays associated with printing, physically sending, signing, and returning documents. For example, Yamaha Motors Philippines used Lexagle to digitize its signing workflows, reducing contract signing times from 2–3 weeks to the same day for urgent requests.
Moreover, signing via digital signatures can also lead to direct cost savings. By minimizing manual administrative tasks, eliminating printing costs, and removing the need for physical document handling (e.g., courier services), organizations can lower the costs of their operational overhead.
Sign Contracts Faster with Lexagle
Get signatures without manually chasing signers. Sign anytime, anywhere while keeping every signed agreement secure.